AI Contract Review Platform
Contract review software for the music industry. Artists and managers upload a recording, management or publishing contract and get a structured risk analysis in minutes.
A live product. Analysis in minutes.
- Client
- Music-industry legal tech (anonymized)
- Product
- Live SaaS, marketing site and app
- Role
- Full-stack developer (sole developer)
The problem
Music contracts are dense, high-stakes and usually reviewed under time pressure. Artists and managers sign recording, management and publishing deals without a clear picture of what they are agreeing to. Full legal review is slow and expensive enough that many skip it.
What we built
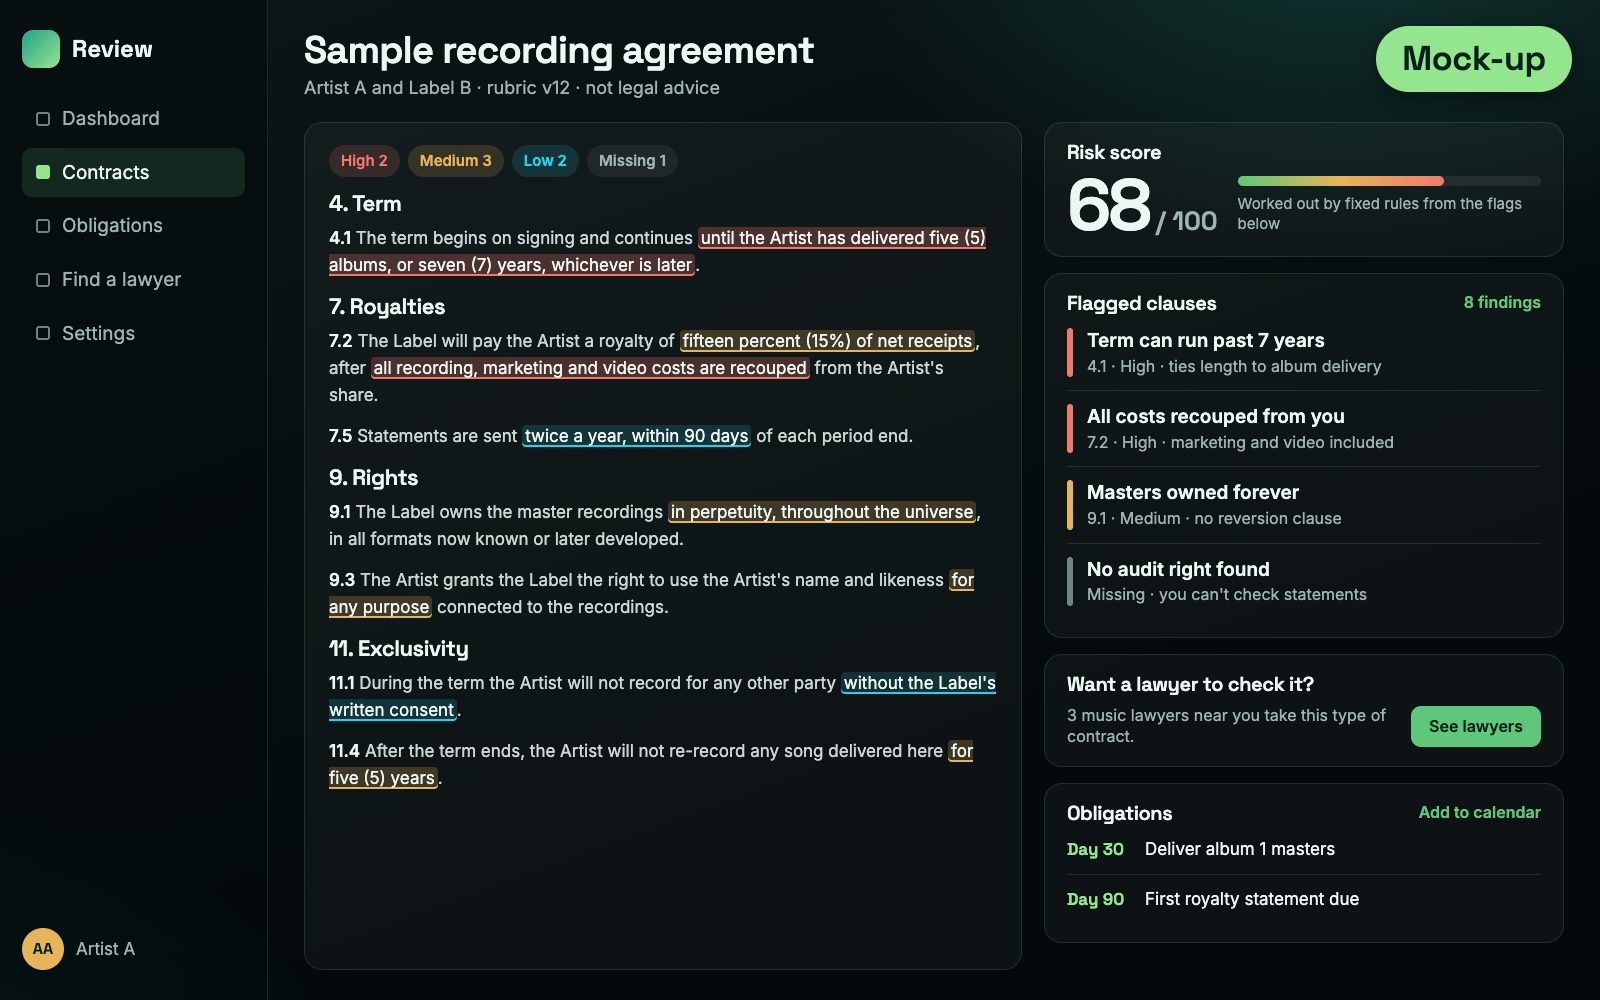
A platform that gives a first-pass, professional-grade analysis in minutes: flagged clauses with severity ratings, evidence highlighted in the document, obligations turned into calendar reminders, and an overall risk score. When a real entertainment lawyer is needed, it connects the user with one.
It is a review tool, not legal advice, and says so clearly next to the route to real counsel.
Features
- The app. Sign-up and log-in with email confirmation and password reset, role selection (artist, manager, lawyer), session middleware, a dashboard, a contract vault with 12-month expiry handling, and settings.
- Contract upload. Drag-and-drop upload to object storage through presigned URLs, text extraction for PDF, DOCX and legacy DOC, and language detection.
- Analysis engine. Tests each contract against a curated library of 102 expert-written hypotheses, developed with a music-industry domain expert.
- Background pipeline. Analysis runs as a memoized job (extract, analyze, format, save). Idempotent, retry-capped and concurrency-limited.
- Review screen. The formatted contract beside a findings rail, severity filter pills, plain-English explanations, and evidence quotes fuzzy-matched and highlighted in place, even inside markdown tables and headings.
- Obligations tab. Pulls out the commitments and deadlines buried in the contract and turns them into calendar actions.
- Payments and tiers. Stripe Checkout for one-off reviews, subscriptions for the Pro tier, the Customer Portal, and a webhook handler keeping access in sync behind a free-tier allowance.
- Lawyer directory. Profiles with specializations, jurisdictions and rates, a contact-request flow tied to specific contracts, and transactional email.
- One product, two subdomains. The marketing site and the signed-in app run on separate subdomains, with auth entry points, CORS and session flow built so they read as one product.
- Groundwork for live collaboration. A Tiptap and Hocuspocus (Yjs) editor server for redlining together, gated to higher tiers.
Stack
- Next.js 14 (App Router)
- TypeScript
- Supabase + RLS
- AI models
- Inngest
- Stripe
- Resend
- Tailwind CSS
How it works
Hypotheses, not "find problems"
The engine doesn't ask a model to find issues. It tests each contract against expert-written hypotheses about what a fair music contract should and shouldn't contain, and marks each one entailed, contradicted or not mentioned.
The model classifies, the code scores
Risk scores come from a fixed flag-weight table over the hypothesis results, so they are explainable and comparable across contracts. A deliberate move away from letting a model guess the score.
Missing protections get flagged
Every hypothesis is tested on purpose, so a protection that simply isn't in the contract shows up as a finding. A "spot the bad clause" prompt would pass right over it.
Versioned rubric
The hypothesis library is content-hashed, so every analysis records exactly which rubric produced it. The same contract gets the same rubric every time, and past results stay readable.
Prompt caching and parallel calls
The contract goes into the model's prompt cache once. Three sharded analysis calls, plus formatting and obligation extraction, then reuse it in parallel. The contract text is paid for once, a big cut to both wait time and token cost.
Retry-safe orchestration
Every expensive step is memoized, with an idempotency check up front, retry caps and singleton concurrency. A retry never redoes finished work and never double-bills. Built after learning what an unguarded retry storm costs.
Evidence you can see
Quotes are fuzzy-matched back into the formatted contract and highlighted in place, so a user can check each claim against the source text instead of trusting a summary.
Security
Row Level Security on all seven tables, service-role access only in server-side jobs, Zod validation on every API payload, strict TypeScript with no any, and secrets only in environment variables.
Results
Minutes
from upload to a full risk analysis
102
expert-written hypotheses in the rubric
A live SaaS product, marketing site and signed-in app, running the full path from upload through analysis, review, obligations, payment and lawyer referral. Every risk score is deterministic: worked out by code, not guessed by the model.
Our role
One developer across the whole product: auth and data model, upload and extraction, the analysis engine and its scoring rubric, the background pipeline, the review screen, Stripe billing and tier gating, the lawyer directory, transactional email and deployment. The hypothesis library was developed with a music-industry domain expert.
About this case study
Client anonymized for privacy: product name, domains and identifying details removed. The screen shown is a mock-up with made-up data. More technical detail available under NDA on request.
Planning a build?
Book a discovery call. 30 to 45 minutes, then a proposal within 3 to 5 business days.